
Financial technology and digital asset firms were early adopters of distributed working, with developers, support staff, and compliance teams spread across homes, shared offices, and time zones. That flexibility brings a security challenge that a single headquarters never faced: every laptop on every kitchen table becomes part of the company perimeter. Teams in the sector have responded with strict habits, hardware security keys for important accounts, separate devices or profiles for sensitive work, encrypted communications, and automatic updates enforced rather than requested. Regular short training sessions keep staff alert to phishing messages that imitate colleagues, exchanges, or customers asking for urgent help with accounts and transfers. New joiners receive this training in their first week, before they receive access to sensitive systems, because habits formed early are far easier to maintain under real pressure later.
What the Evidence Shows
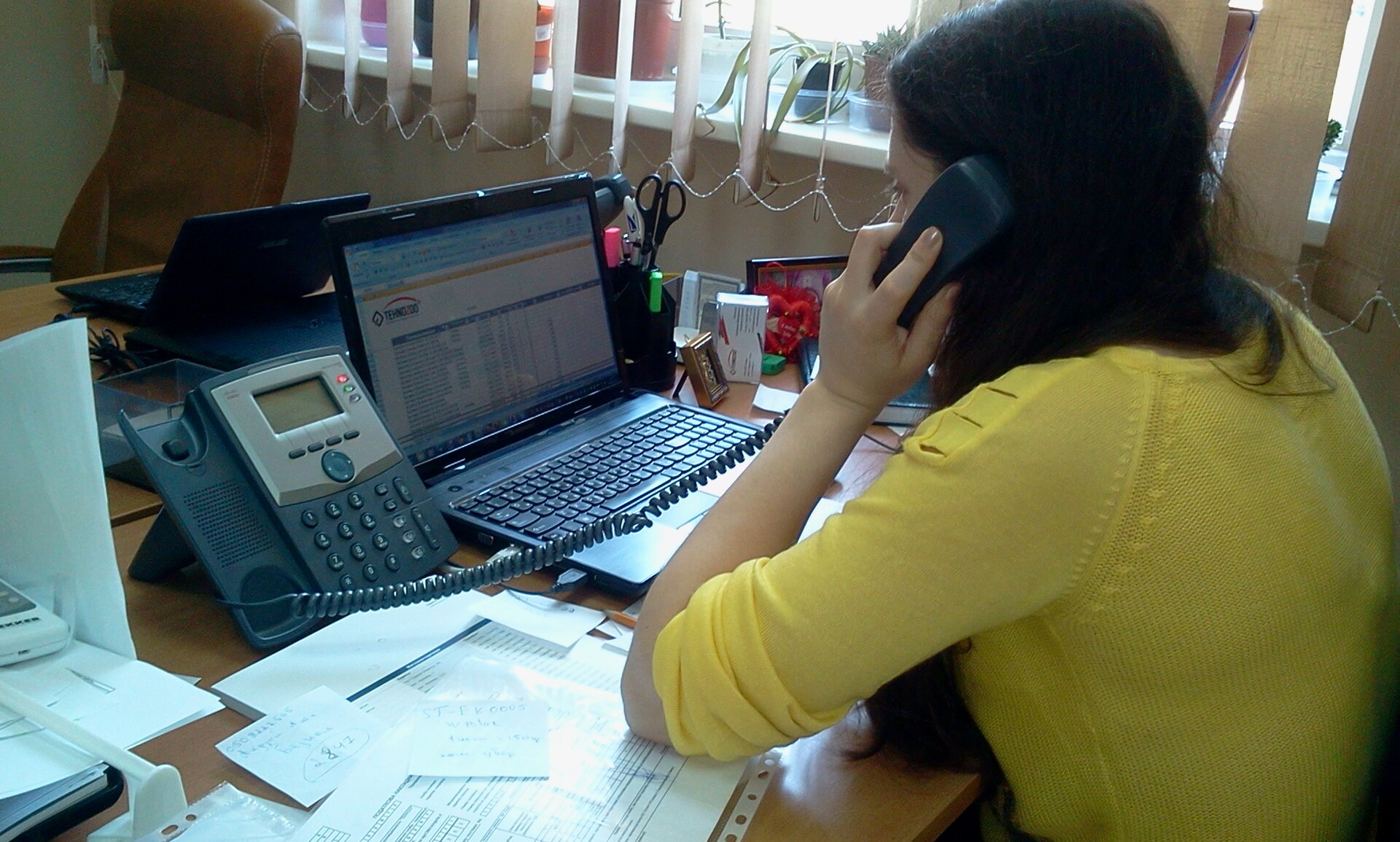
The culture around those tools matters as much as the technology. Staff are encouraged to verify unusual requests through a second channel, to report suspicious messages quickly without embarrassment, and to treat delays for security checks as normal rather than obstructive. Managers schedule overlap hours so that important approvals never rest on one tired person working alone at night. For customers, none of this is visible, yet it underpins whether a platform keeps operating safely through attempted attacks that arrive daily. As remote work settles into a permanent pattern across finance, the laptop in the photograph is no longer just an office tool; it is where the office itself now happens. Written incident procedures, rehearsed occasionally like a fire drill, ensure that if a laptop is lost or an account is targeted, the response is calm, quick, and already decided. Reporting and analysis from sources such as European Central Bank track the same developments, and specialists following security habits for distributed fintech teams say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is a sector being absorbed, piece by piece, into the regulated financial mainstream. Work on security habits for distributed fintech teams now happens under licensing regimes, audit expectations and consumer-protection rules that would have been unrecognisable a few years ago. Long-standing participants are divided between relief at the legitimacy and regret for the experiment’s wilder freedoms.
What Happens Next
What happens next for security habits for distributed fintech teams will be shaped by the interaction of regulation, market appetite and the sector’s own capacity for self-inflicted wounds. The infrastructure is more professional than it was, the rules are clearer, and the remaining question is whether growth can stay boring. Participants with the longest memories say boring would be the real milestone. You can follow related developments in our coverage of crypto.
None of this will be settled by a single announcement, study or product launch. The pattern to watch is accumulation: independent confirmations, honest reporting of failures and steady improvement in the underlying numbers. Readers who follow those signals, rather than the loudest claim of the week, will understand this subject better than most of the commentary surrounding it suggests is possible.